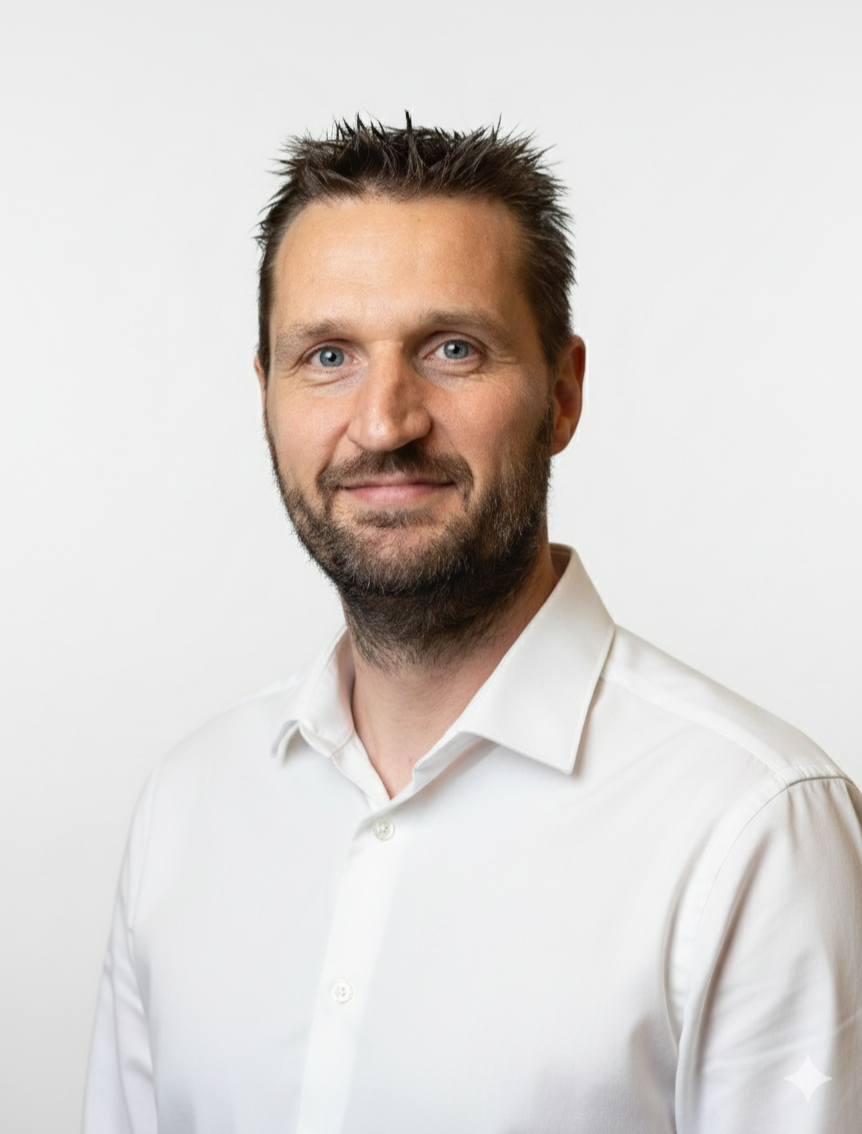
Bas Volkers

Founding and Managing Partner,

Security and Governance

Bas works with boards and leadership teams to establish executive grade security governance.
More info
Bas works with boards and leadership teams to establish executive grade security governance: a clear baseline, explicit decision rights and ownership, and an operating cadence that keeps evidence current between audits and change.

He brings 20+ years in organisational improvement and programme control and 15+ years in information management and security, including interim CISO work in complex environments (universities and large organisations) and ISO 27001 and ISO 9001 implementation.

Focus areas
  • Security governance and ISMS build and scale
  • Board ready risk decisions, ownership, and evidence
  • Orchestrating specialists and tools with explicit handoffs

The team

Information Security officers,

Business Consultants

Our team consists of information security specialists  that speak the language of the business.

More info
 Our consultants combine deep expertise in information security, ISO 27001 and NIS2 with the ability to bring clarity, structure and accountability to complex organisations.

They identify where responsibilities are unclear, where risks are insufficiently understood and where governance is failing to deliver effective control.

By translating technical and regulatory requirements into clear management decisions, practical improvements and measurable outcomes, they help organisations understand their real risks, set the right priorities and build information security into everyday operations. 

The result is not more paperwork, but better decisions, stronger control and a more resilient organisation.

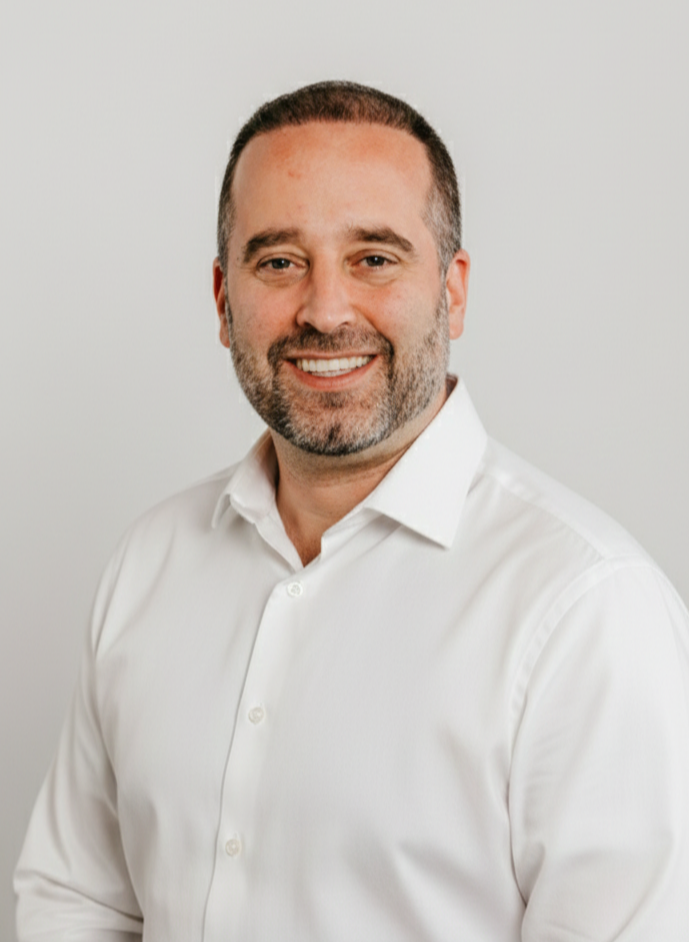
Hans Stenfert Kroese

Managing Partner,

Privacy and Social Engineering

Hans helps leadership teams make privacy and social engineering risks manageable in the real world.
More info
Hans helps leadership teams make privacy and social engineering risks manageable in the real world: clear decisions, practical safeguards, and evidence that stands up to customer and regulatory scrutiny.

As a Data Protection Officer, he supports GDPR requirements through privacy risk assessments, DPIAs, operational privacy governance, and liaison with supervisory authorities. He also helps organisations identify how manipulation, human behaviour, and weak processes can expose personal and sensitive information. Through social engineering assessments and targeted awareness, he turns these risks into practical improvements in behaviour, governance, and control. 

Focus areas
  • Social engineering assessments and human risk
  • DPIAs, privacy risk assessments, and operational privacy governance
  • Awareness and practical safeguards for sensitive information

DISCOVER YOUR ROOT CAUSE SECURITY ISSUES

AND TRANSLATE THEM INTO CLEAR DECISIONS 

Why Flodisq

We bring people, information, processes and technology together to make information security clearer and more actionable. Our specialists combine practical security and governance experience with AI agents that help analyse findings, identify connections and surface underlying risks. This gives organisations a clearer view of what matters, who needs to act and what to do next.

Our values


Radical honesty
and transparency 
with leadership
Independence
 we leave when 
we are no longer needed
Practical rigour
operational reality 
over policy theatre

START WITH A BASELINE CALL

If security and governance are creating recurring disruption, blocked revenue, or board risk, we start with a short baseline call and give you a clear recommendation on what matters, what to do first, and how to keep it current.
Search